- Alerts by volume, not by business risk.
- An audit once a year, and blind the rest of the time.
- Disconnected products, each with its own console and contract.
- Reaction comes once the incident has already happened.
Since 2014 · Operating in 7 countries · CSIRT certified
We contain sophisticated attacks
The ones that outrun conventional tools. We integrate cyber intelligence, cybersecurity, engineering, technology and artificial intelligence to protect organisations against complex threats.
ISO 9001:2015 · ISO/IEC 27001:2022 · FIRST Member
Cybersecurity today has a challenge of integration.
Organisations have already invested in technology. The challenge has moved.
According to the Global Threat Report 2026 by CrowdStrike, 82% of detections involved no malware.
-
Multiple security technologies that do not talk to each other.
-
Data scattered across separate consoles, with no central correlation.
-
Several vendors, each with its own scope and contract.
-
An attack surface that grows with every cloud, every device and every third party.
-
Alert volume beyond the real capacity of the team.
-
24/7 operations hard to sustain in-house with scarce talent.
-
Growing regulatory pressure, with audits and deadlines that do not wait.
The challenge is integrating it all.
From the product to the capability we run.
The market answers with tools. By now, the problem is no longer about tools.
- Operations driven by business risk, not by alert volume.
- Exposure managed continuously, under CTEM.
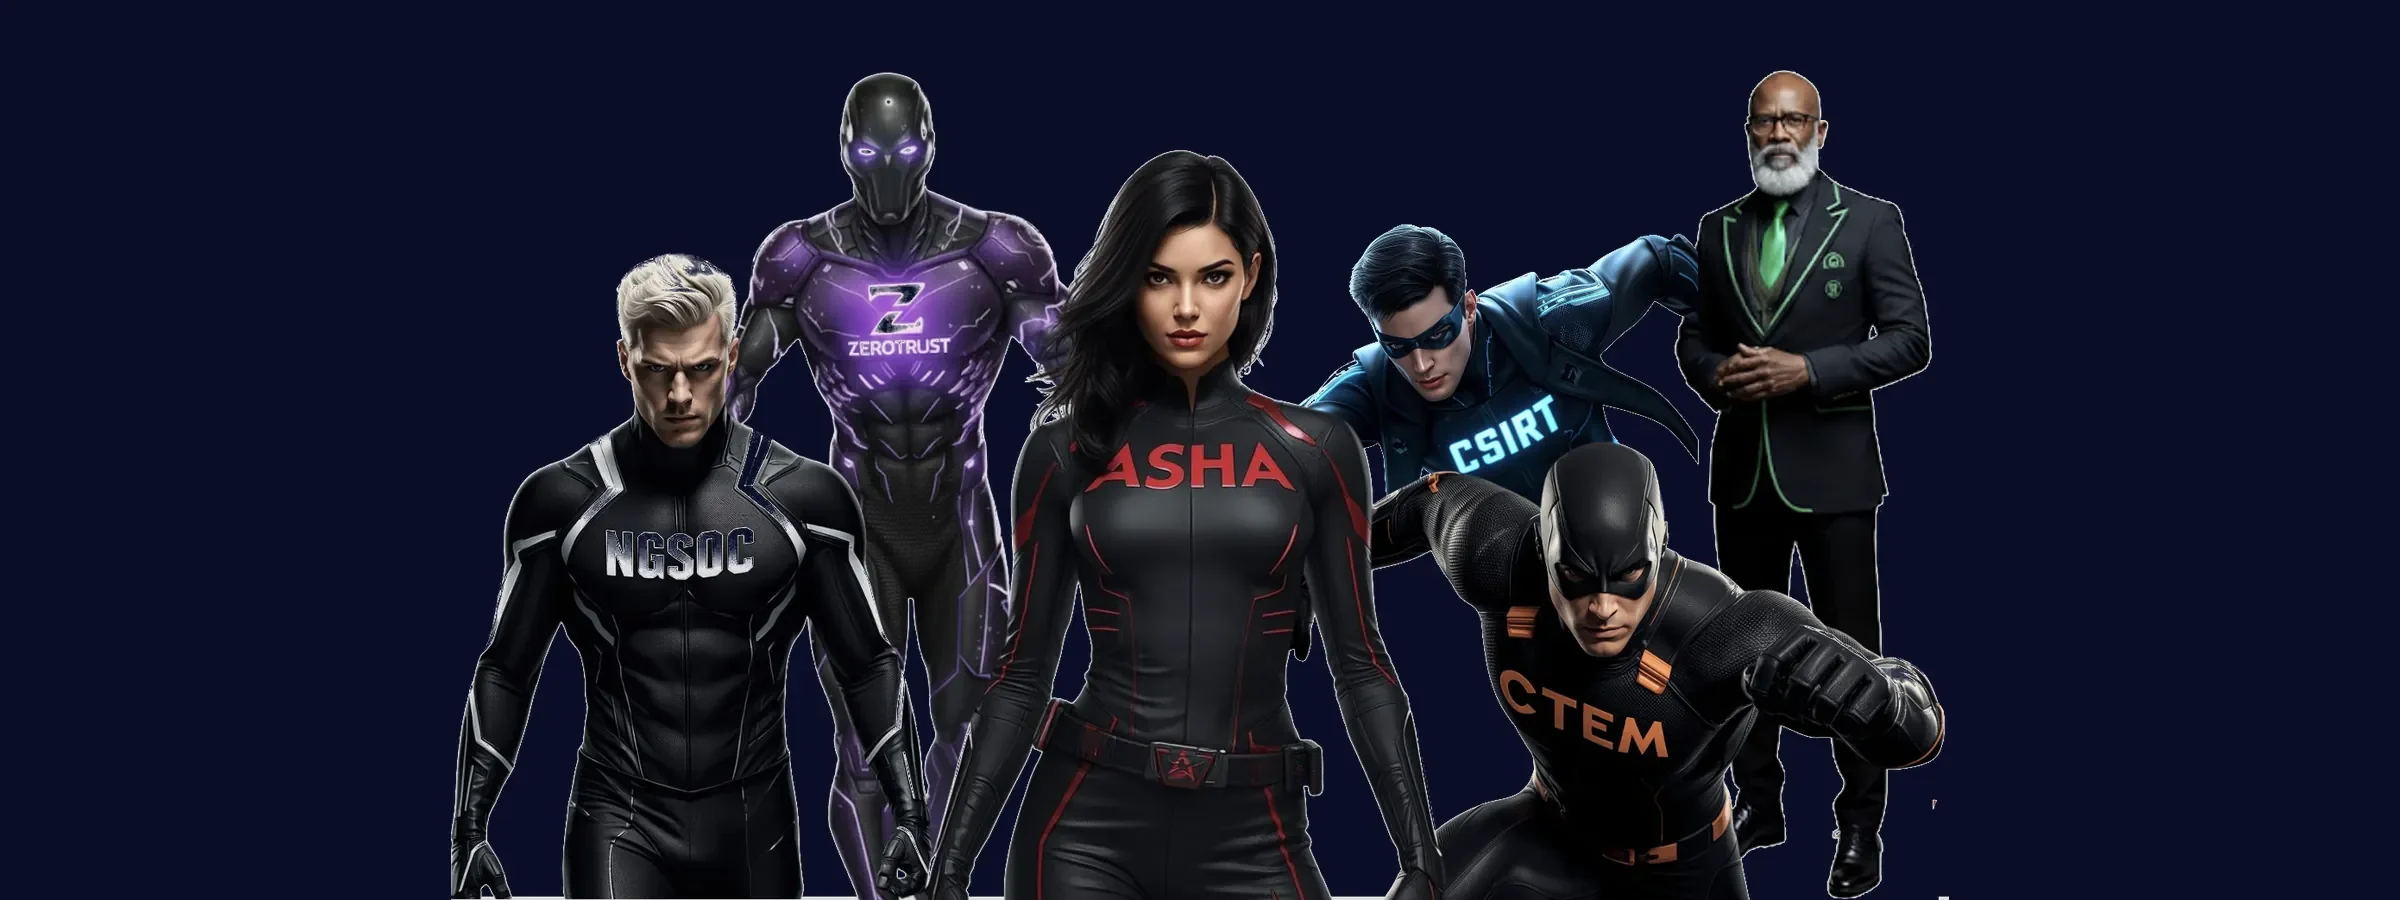
- The Captain and five fronts operating as a single system.
- Anticipation and resilience, not reaction.
One defence system, coordinated as a single whole.
Engineering, technology, five methodologies, integration, artificial intelligence and 24/7 operations, coordinated as a single capability.
01
Orchestrate
ASHA, The captain
The organising principle: it orchestrates the five fronts under our own methodologies, with Scrum, PMP® and ITIL certified leads.
SOC Management ISO 9001 ISO 27001 Meet the captain 02 Anticipate
CTEM
Continuous threat exposure management: IT and OT assets, shadow IT, vulnerability prioritisation and adversary emulation.
TraceWatch
TraceGuard
RedTeaming
MITRE ATT&CK
Meet the hero
03
Detect
NGSOC
Next-generation operations centre with 24/7/365 monitoring, run under the CCIIIAR Plan, ASHA's master plan: Continuous Hunting, AI, Investigation, Integration, Automation and Response.
DataManager
NGSIEM
Continuous Threat Hunting
Meet the hero
04
Investigate
CSIRT ASHA
Investigates the actors behind each threat and traces them back to their sources: verified intelligence, a collaborative MISP platform and escalation to the main global agencies.
Sharing TI
Unified TI+
Fraud Hunting
Digital Forensics
Meet the hero
05
Protect
Zero Trust
Security without a perimeter: explicit verification, least privilege and control over identity, access, applications, networks and data.
Identity
Access control
Applications
Networks and clouds
Data security
Meet the hero
06
Govern
GRC
Governance, risk and compliance: cybersecurity maturity, regulatory gap analysis and risk metrics for boards.
Insight
Enforce
CISO as a Service
Meet the hero
What do you need to solve?
Start by analysing your challenge. We tell you how we handle it, with which methodology and under which operating model.
CTEM
Reduce your exposure
You do not know how many assets you have, nor which expose you most. We identify and prioritise the attack surface across IT, OT and shadow IT, with adversary emulation.
See the CTEM methodology
NGSOC
Modernise your SOC
Alert volume outpaces the team and correlation falls short. We run detection, containment and investigation under the CCIIIAR Plan, ASHA's master plan: Continuous Hunting, AI, Investigation, Integration, Automation and Response.
See the NGSOC methodology
CSIRT
Respond to an incident
You need to investigate, attribute and document. Our own CSIRT with verified threat intelligence, digital forensics and escalation to global agencies.
See the CSIRT methodology
Zero Trust
Protect identities and access
The perimeter is gone and access keeps multiplying, now including AI agents. Explicit verification and least privilege over identity, applications, networks and data.
See the Zero Trust methodology
GRC
Turn risk into decisions
Your board asks for figures, not incidents. Maturity, regulatory gap analysis, Shadow AI under control and sovereignty over your data: risk metrics that support an investment decision.
See the GRC methodology
Engineering and integration
Integrate your ecosystem
You have the tools, but they do not talk to each other. We design the architecture, connect consoles and sources, and automate the response.
See how we operateAI-automated attacks are now almost instant.
So is our response.
From strategy to operations.
We do not stop at the recommendation: we design the architecture, integrate it, deploy it and operate it.
- Assess
- Design
- Integrate
- Deploy
- Operate
- Optimise
-
Project office and ongoing support
To make sure the technologies, solutions and practices pay off, we provide managed services or support services, with a PMO watching over quality.
-
Engineering and processes
Our highly qualified engineering team tunes methodologies, regulatory and reference frameworks, along with the technology and processes needed to secure success.
-
Technology
We partner with the most recognised and forward-looking brands on the market, as well as the most disruptive and innovative ones, pioneering their successful use.
-
API development, KPI dashboards and integrations
Our specialists improve the vendors’ APIs and look for ways to integrate our offering further, with KPIs and analytical dashboards for our services.
Leaders in their categories per industry analysts
 CrowdStrike
 Netskope
 Proofpoint
 OKTA
 Fortinet
 Imperva
 ForescoutCrowdStrikeNetskopeProofpointOKTAFortinetImpervaForescout
Niche solutions
 Cribl
 Kriptos
 Group-IB
 StrangeBee
 Reveald
 Automox
 Tenable
 Thales
 Broadcom
 DarkivoreCriblKriptosGroup-IBStrangeBeeRevealdAutomoxTenableThalesBroadcomDarkivore
Success stories
Measurable results
Measurable results
in production.
Real migrations to CrowdStrike NextGen SIEM with ingestion tuning, data governance and a proactive posture.
NextGen SIEM live in 3 weeks
Before
Limited visibility, technologies with no central correlation and slow manual response, with high MTTD, MTTC and MTTR.
After
Curated source migration from IBM QRadar to CrowdStrike NextGen SIEM: immediate detection, proactive threat hunting and Falcon Fusion SOAR with AI/ML rules.
122
integrated sources
800GB/day
managed ingestion
−50%
optimised ingestion
365days
hot retention
From Splunk to NextGen SIEM with Data Manager
Before
Every technology ingested unfiltered, licensing growing exponentially and a team swamped by context-free events, with obsolete use cases.
After
CrowdStrike NextGen SIEM with Data Manager: tuned ingestion, cleared alerts, an up-to-date use-case matrix and full governance of data and events.
−30-40%
of the ingestion from key sources
Data Manager
full data governance
Proactive
threat hunting and our own use cases
Key industries
Deep experience across regulated and critical sectors
- Financial services
- Insurance
- Retail
- Manufacturing
- Energy
- Healthcare
- Aviation
- Services
- Public sector
- Industry
- Construction
95% coverage across regulated and critical sectors: financial services, insurance, retail, manufacturing, energy, healthcare and aviation.
12+ years protecting banking, insurance and retail. Operations aligned with ISO 27001, PCI DSS and local regulations, audited and repeatable country by country.
In manufacturing and construction we work across heterogeneous attack surfaces (IT + OT + cloud) and different regulatory exposure.
We operate across LATAM and are expanding into more markets
Local subsidiaries in the countries where we operate. Monitoring centres in Mexico City and Tenerife running 24/7, with global time coverage.
Active operations
In development
Monitoring centre
Active operations[ 7 ]
- Mexico2014
- Chile2020
- Ecuador2022
- Dominican Republic2022
- Colombia2024
- Peru
- Panama
Monitoring centre[ 2 ]
- CDMX7×24
- Tenerife7×24
Managed services and MDR validated by the vendors under MSSP contracts, with global time-zone coverage.
Sector CSIRT
Insurance and Financial, Mexico
Built and run by ASHA, expanding to more countries in the region.