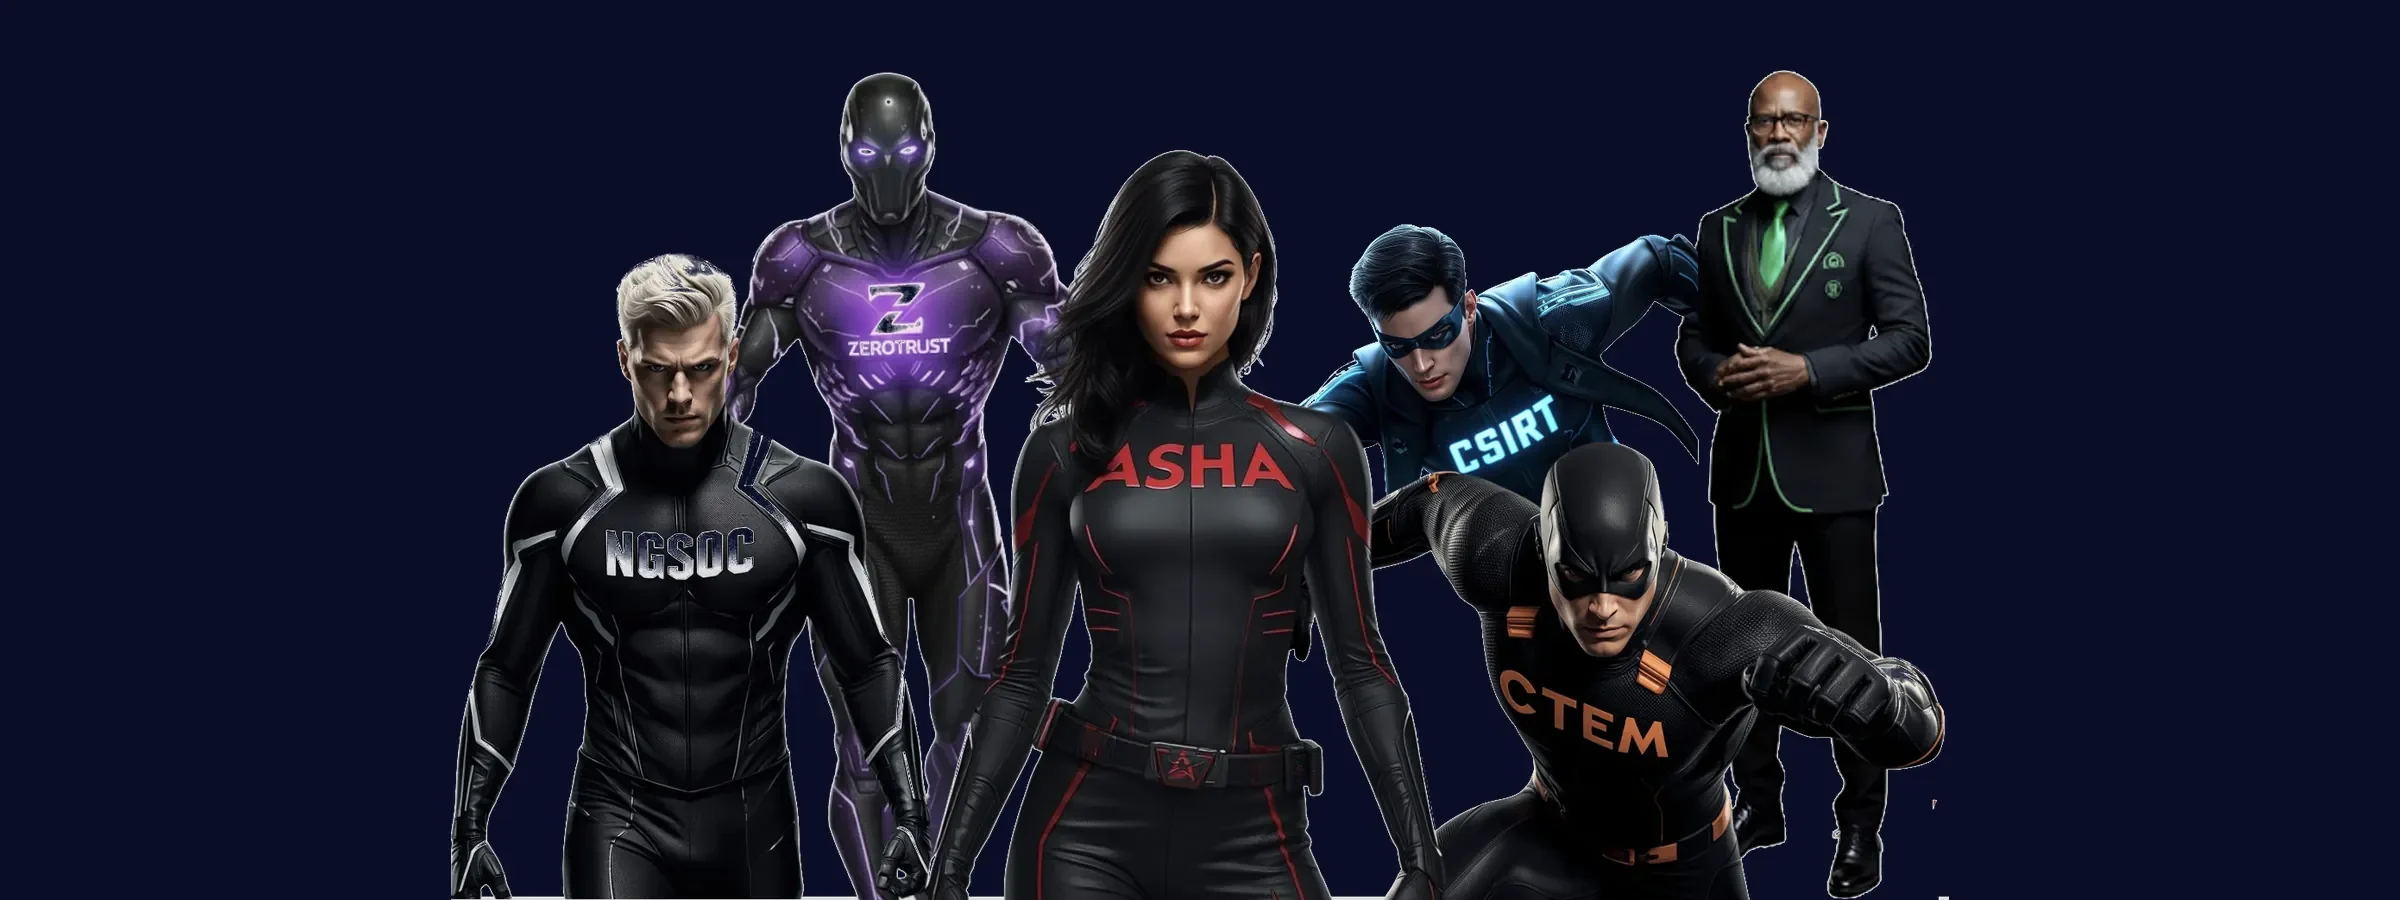
Methodologies embodied as superheroes
As threats keep evolving, we turned our methodologies into superheroes, six lines of defence, each with its own mandate, frameworks and services.
Orchestrate · Leadership and end-to-end protection
ASHA

The organising principle of the universe. ASHA stands for our conviction to do things right, from design to execution, orchestrating the five fronts under our own methodologies.
- The “as it should be” philosophy applied to operational design
- Operating models that protect the business and build trust
3
Technical services
See the detail
- ASHA Value Delivery PMO
- Our own methodological model for project management, built on value and quality.
- Project Leadership
- Scrum, PMP® and ITIL certified project leaders · hybrid frameworks aligned with ITIL good practice
- Quality Assurance
- Operating under ISO 9001:2015 and ISO 27001:2022 · annual audits · complete service cycles
Anticipate · Continuous threat exposure
CTEM

Continuous Threat Exposure Management. It finds gaps, prioritises with threat intelligence and emulates real adversaries to validate the effective resilience of IT and OT environments.
- Vulnerability prioritisation with Threat Intelligence
- Full MITRE ATT&CK · Cyber-Kill Chain coverage
5
Technical services
See the detail
- TraceWatch
- IT and OT asset management · discovery of unmanaged assets · shadow IT · prioritisation with threat intelligence
- TraceGuard
- Threat exposure management · insecure configurations in exposed applications and services · technology risk management · vulnerability remediation management · monitoring of compromised credentials and accounts
- RedTeaming
- Attack path creation · adversarial simulations · MITRE ATT&CK emulations
- Vulnerability Management
- Identification of vulnerabilities, risks and impact on assets and infrastructure
- Self-assessment
- Penetration testing · compromise assessment · control audits · security awareness
Integrate · Security operations
NGSOC

Next-generation security operations centre. Real-time data ingestion, parsing and enrichment, MITRE ATT&CK-based use cases and automated response.
- Run under the CCIIIAR Plan, ASHA's master plan: Continuous Hunting, AI, Investigation, Integration, Automation and Response
- Operational target aligned to MITRE ATT&CK: detection in 1 min, investigation in 10 min, response in 60 min
- Integration of critical vectors: CrowdStrike, Netskope, DarkTrace, Nozomi (OT), PAM360 and Harmony
- MITRE ATT&CK and NIST 2.0 based use cases · 24/7/365 monitoring with analysts
6
Technical services
See the detail
- NGSIEM
- Native and custom integrations · real-time ingestion, parsing and enrichment · use cases built on MITRE ATT&CK and NIST · advanced correlation and automated response · dashboards and actionable intelligence · 24x7x365 monitoring with analysts
- DataManager
- Architecture, orchestration and efficiency in data handling · scalable mass storage · multi-source governance · hybrid pipelines (on-prem + cloud) · cost optimisation
- Continuous Threat Hunting
- Continuous and proactive hunting · managed response · AI applied to anomalous behaviour analysis · threat intelligence correlation · advanced analysis with Tableau, Python and Grafana · feeds the NGSIEM use-case matrix
- Architecture & Engineering
- SOC architecture · engineering practices · control and inventory standards
- Log Management
- Collection, processing and storage from multiple sources
- Incident Monitoring
- Identification, classification, prioritisation, analysis and notification of incidents
Investigate · Intelligence and incident response
CSIRT

Computer Security Incident Response Team with our own collaborative platform. Verified threat intelligence, MISP sharing and escalation to the main global security agencies.
- Managed and co-managed services validated as MSSP
- Specialised local teams aligned to FIRST · escalation to global agencies
7
Technical services
See the detail
- Sharing TI
- Intelligence sharing on the MISP platform · investigations · bulletins · aligned with FIRST
- Unified TI
- Brand protection · attack surface analysis · detection of compromised accounts
- Unified TI+
- Data Breach Protection · Tactical Threat Intelligence · Digital Footprint Protection · Impersonation & SOCMINT
- Fraud Hunting
- User behaviour monitoring · user impersonation · transactional fraud · account takeover · fake account creation
- Incident Response
- Post-detection management · containment, eradication and recovery · aligned with NIST SP 800-61
- Threat Intelligence
- Planning, collection, processing, analysis and dissemination of actionable intelligence
- Digital Forensics
- Identification, acquisition, processing and analysis of digital evidence from incidents and attacks
Protect · Identity and access
Zero Trust

A security model without a perimeter. It verifies every access explicitly, assumes breach and enforces least privilege across identity, device, network, application and data.
- Verify every access explicitly · assume breach · least privilege
- Six domains: identity, access, applications, networks, data and AI
6
Technical services
See the detail
- Identity
- Identity hygiene · identity and access management (IAM) · multi-factor authentication (MFA)
- Access Control
- Micro-segmentation · ZTNA · attribute-based access · SD-WAN · Digital Experience
- Applications
- CASB · Web control · WAF · DB Firewall · AI and API security
- Networks and cloud
- NGFW · NTA · SSE · Cloud Security · security posture
- Data security
- DLP · classification and inventory · data governance
- Protection against AI
- A strategy for the use and the protection of AI.
Governance, risk and compliance
GRC

It raises cybersecurity maturity and secures regulatory compliance. Continuous programmes, board-level metrics and CISO as a Service to support executive decisions.
- Raises cybersecurity maturity and secures regulatory compliance
- Actionable KPIs, KRIs and risk metrics for boards
3
Technical services
See the detail
- Insight
- Maturity assessment for cybersecurity strategies · risk map over attack vectors · growth strategy · regulatory GAP analysis (ISO 27001, PCI DSS, NIST 2.0, GDPR) · life cycles for data and identity
- Enforce
- Development and implementation of policies, procedures and controls · external audits (ISO 27001, ISO 9001) · risk remediation plans · user training and awareness
- CISO as a Service
- Raising maturity and regulatory compliance · continuous GRC programmes · compliance reporting and monitoring · KPIs / KRIs for boards